IT Governance & Risk Review
Assessment of technology oversight, decision rights, policies, risk ownership, performance monitoring and alignment between IT activities and organizational objectives.
Independent assurance over technology, data and digital controls—so leaders can act on risk with confidence.
How we create value
An effective IT audit does more than review technical settings. It evaluates whether governance, people, processes, applications, infrastructure and data work together to protect operations and support reliable decisions.
Service scope
The exact scope is shaped around the organization, assignment objectives, available information and required outcomes.
Assessment of technology oversight, decision rights, policies, risk ownership, performance monitoring and alignment between IT activities and organizational objectives.
Review of the foundational controls that support reliable system operation.
Evaluation of controls within selected business applications to assess whether transactions and data are authorized, complete, accurate and processed as intended.
A risk-based review of governance and selected protective, detective and response controls across the agreed technology environment.
Assessment of how access is requested, approved, provisioned, modified, monitored and removed, including privileged access and segregation-of-duties considerations.
Review of data ownership, quality, interfaces, reconciliations and reporting logic, supported where appropriate by data analysis and computer-assisted audit techniques.
Assessment of continuity governance, backup arrangements, recovery objectives, testing, dependencies and readiness to restore critical technology-supported services.
Independent review before or after implementation of a major ERP, accounting, HR, project or operational system, covering governance, controls, data migration, testing, cutover and readiness.
Review of governance, cost, schedule, risk, reporting, data and control arrangements across technology-enabled projects or project management information systems.
Assessment of governance and control considerations for cloud services, outsourced processing, technology vendors and other critical service providers.
Review of needs assessment, specifications, evaluation, contracting, acceptance, asset control and vendor oversight for selected technology acquisitions.
Support to organize evidence, map controls, assess known gaps and establish a practical remediation plan before an external, regulatory, customer or internal review.
Focused procedures designed around a defined technology concern, transaction population, control area or management question, with factual findings reported against the agreed scope.
Assignment outputs
Deliverables vary with the engagement. A scope may include one focused output or an integrated package of analysis, tools and implementation support.
How we work
A disciplined process keeps the work focused on evidence, practical decisions and outcomes management can act on.
Confirm the systems, business processes, stakeholders, objectives and assurance questions within scope.
Identify critical information assets, dependencies, threat scenarios and areas of potential control failure.
Document relevant governance, general, application, security, data and project controls.
Gather and evaluate evidence through interviews, documentation, walkthroughs, configuration review, sampling and data analysis as appropriate.
Explain findings, business impact, root cause and priority in clear management language.
Agree practical corrective actions, accountable owners and a realistic remediation sequence.
Organizations we support
Our engagement model can be adapted to focused assignments, recurring support or broader multidisciplinary requirements.
We connect technology controls with financial reporting, operations, governance and compliance.
Engagements can cover an enterprise environment, one application, a technology project or a defined control domain.
Findings are organized around risk and business impact so management can focus resources where they matter most.
Reports can be supported by control matrices, action plans and follow-up reviews to help improvements move forward.
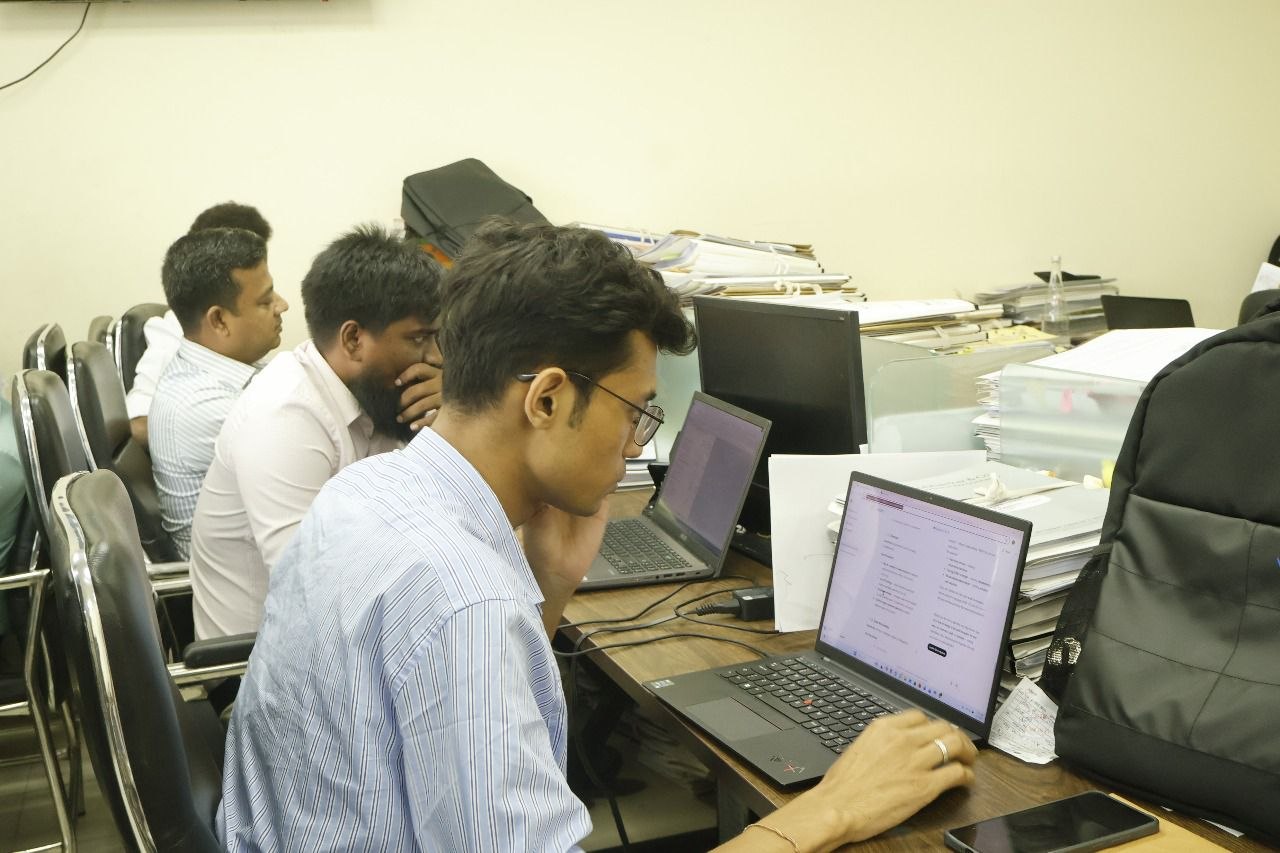
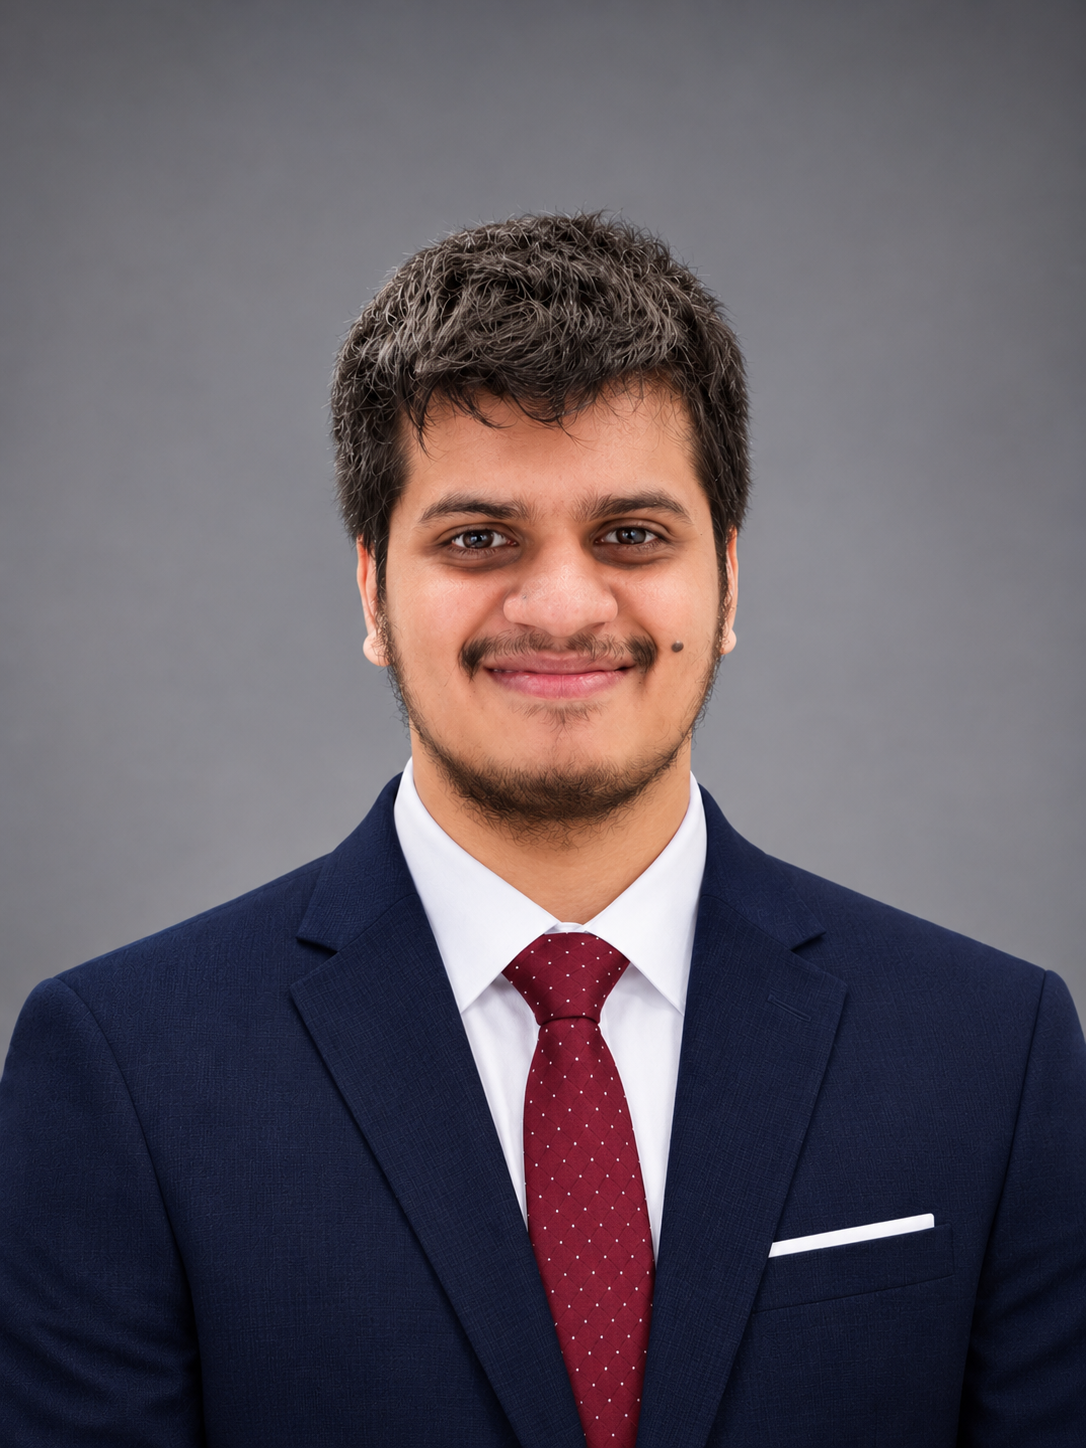
IT Audit team
Engineering perspectives supporting technology-focused assurance, digital controls and organizational risk.
Useful answers
A few common questions about the service and how an engagement can be structured.
The JKMNS difference
A multidisciplinary professional platform built around context, implementation and long-term organizational value.
Financial, operational and organizational issues rarely exist independently. JKMNS brings together expertise across audit, tax, accounting, corporate advisory, governance, HR, technology, development consulting and sustainability.
We focus on solutions that management can understand, implement and monitor—not recommendations that remain in a report.
Our work is grounded in financial information, documentation, stakeholder evidence, analysis and professional judgment.
We understand the practical operating, regulatory, institutional and business environment in which organizations in Bangladesh operate.
Where required, we support clients beyond diagnosis through policies, procedures, models, templates, dashboards, training and implementation roadmaps.
We recognize the sensitivity of organizational, financial, employee and strategic information and maintain disciplined engagement and documentation practices.
A clear beginning
Tell us what your organization needs to achieve or what problem you are facing.
We define objectives, required work, information requirements, deliverables and expected timeline.
JKMNS provides an engagement proposal reflecting the agreed scope.
Our team works with designated client stakeholders and maintains structured communication throughout the assignment.
Findings and deliverables are discussed with management so implications and recommended actions are clearly understood.
Integrated support
Many organizational challenges require integrated support. JKMNS can structure multidisciplinary engagements around the underlying requirement rather than treating every issue separately.
Explore our connected servicesAn accounting assignment may identify tax issues.
An audit may identify internal-control gaps.
A restructuring may require financial modelling and HR redesign.
Digital transformation may require process and governance improvements.
An ESG programme may require data, risk and reporting systems.
Let’s make the difference
Whether you need an enterprise IT controls review, assurance over one critical application, a system implementation review or focused technology project oversight, JKMNS can shape the engagement around your risk and governance priorities.